
Security vulnerability at biggest gym chain in South Africa

A serious vulnerability in Virgin Active South Africa’s payment systems has been revealed, potentially exposing private client information, including bank account details.
Cybersecurity analyst and ethical hacker Bruce Malaudzi reached out to MyBroadband with the information that a critical flaw in the gym’s Netcash payment systems could be exploited by threat actors.
MyBroadband helped him disclose his findings to Virgin Active, whose security personnel patched the vulnerability over the weekend.
With 125 clubs and 631,000 members across South Africa, Virgin Active is the country’s largest gym chain.
Malaudzi explained that he found the vulnerability through a routine link Virgin Active sends customers to make payments. He said he could tell something was wrong when he first looked at the link.
“As a senior cybersecurity professional, I could tell that the payment link system’s security is enforced at the client side, instead of server side,” he told us.
“This means a client can manipulate the URL or HTTP query, and the server accepts it.”
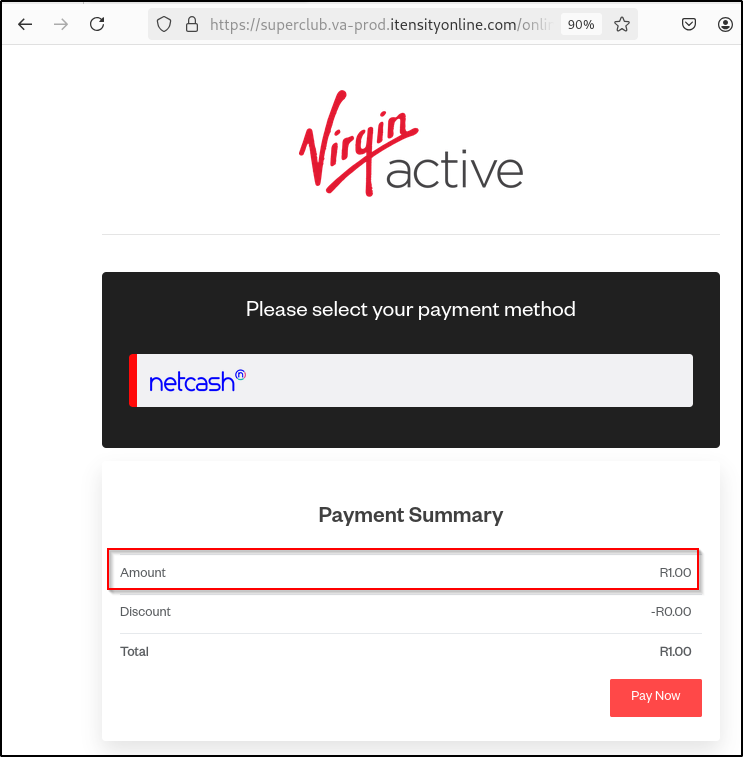
Malaudzi provided us with code and screenshots showing how an attacker could easily change the amount owed to a specific client by exploiting this client-side payment link.
He did this simply by manipulating the URL in the link sent to clients by Virgin Active when requesting payment, for example, if a client’s monthly payment bounces.
Malaudzi demonstrated that users can change how much any gym member owes at any given time. For example, a user who owed R2,200 could reduce their bill to R1 with the exploit.
The nature of the vulnerability meant that any user with rudimentary coding knowledge could change their monthly bill to R1 every month. A Premier membership at the gym chain costs R1,670 per month.
While potentially damaging for the company, this exploit came with a more serious problem. A hacker could use it to continue digging into the system and find private user information.
“If you visit any of the links mentioned earlier and switch to Developer Tools on your browser, you will see a hardcoded API key,” Malaudzi said.
“With this token, you can query the backend database.” Essentially, a hacker could dump user information for every Virgin Active member in the entire country, en masse.
This includes information on how much money they owe the gym chain and their email addresses, at first. Malaudzi said he could also obtain the names of every single sales consultant in the country.
A very serious problem for Virgin Active

He said that he did not continue digging into the system because it would have been illegal to do so without written permission from Virgin Active. However, the law would not stop a cybercriminal.
Using the same vulnerability, a threat actor can uncover personally identifiable information from gym members, including any details they provided when signing up. That includes bank account details.
Criminals can also use the information to conduct highly-targeted “spear phishing attacks,” where users are lured into clicking malicious links.
“Knowing the exact amount owed (R1425.0) and the member’s gym (Virgin Active – Kings Park) allows an attacker to send a fake payment link that a victim is highly likely to trust,” Malaudzi says.
No private Virgin Active member information exposed


Virgin Active was unaware of the vulnerability when we contacted them on 18 March 2026.
“Upon receipt of your email, we took immediate precautionary action by disabling the relevant payment links while our IT and security teams investigated the matter,” the company told MyBroadband on Monday.
“The review identified a number of lower-risk items requiring attention, which were addressed on the same day.” Virgin Active said it has now implemented enhancements to the payment link functionality.
“There are some residual elements related to previously issued links that are currently being finalised as part of this process,” it said.
“Based on our assessment to date, we are satisfied that no sensitive information has been exposed and that appropriate controls are in place.” Virgin Active said protecting member information remained a top priority.
“We take matters of this nature very seriously. We will continue to monitor and review our systems as part of our ongoing security and risk management processes.”


 Loading ...