


Gordon_R
Honorary Master
This was flagged back in August, this has a break-down of the exploit:
Freeze the Controller, Defrost the Food: Uncovering Vulnerabilities in Danfoss Refrigeration Controllers
Team82 researched the attack surface of the Danfoss AK-SM 800A refrigeration controller platform and identified multiple vulnerabilities affecting the embedded web management interface. Team82 disclosed the vulnerabilities to Danfoss, which addressed them in a new firmware version. Successful...claroty.com
Still a bit crazy that this was directly on the internet as well, this should at least have been on an internal one. Doesn't matter that the device can't be patched, should have been taken off of the internet, this is going to be interesting to see if insurance pays out.
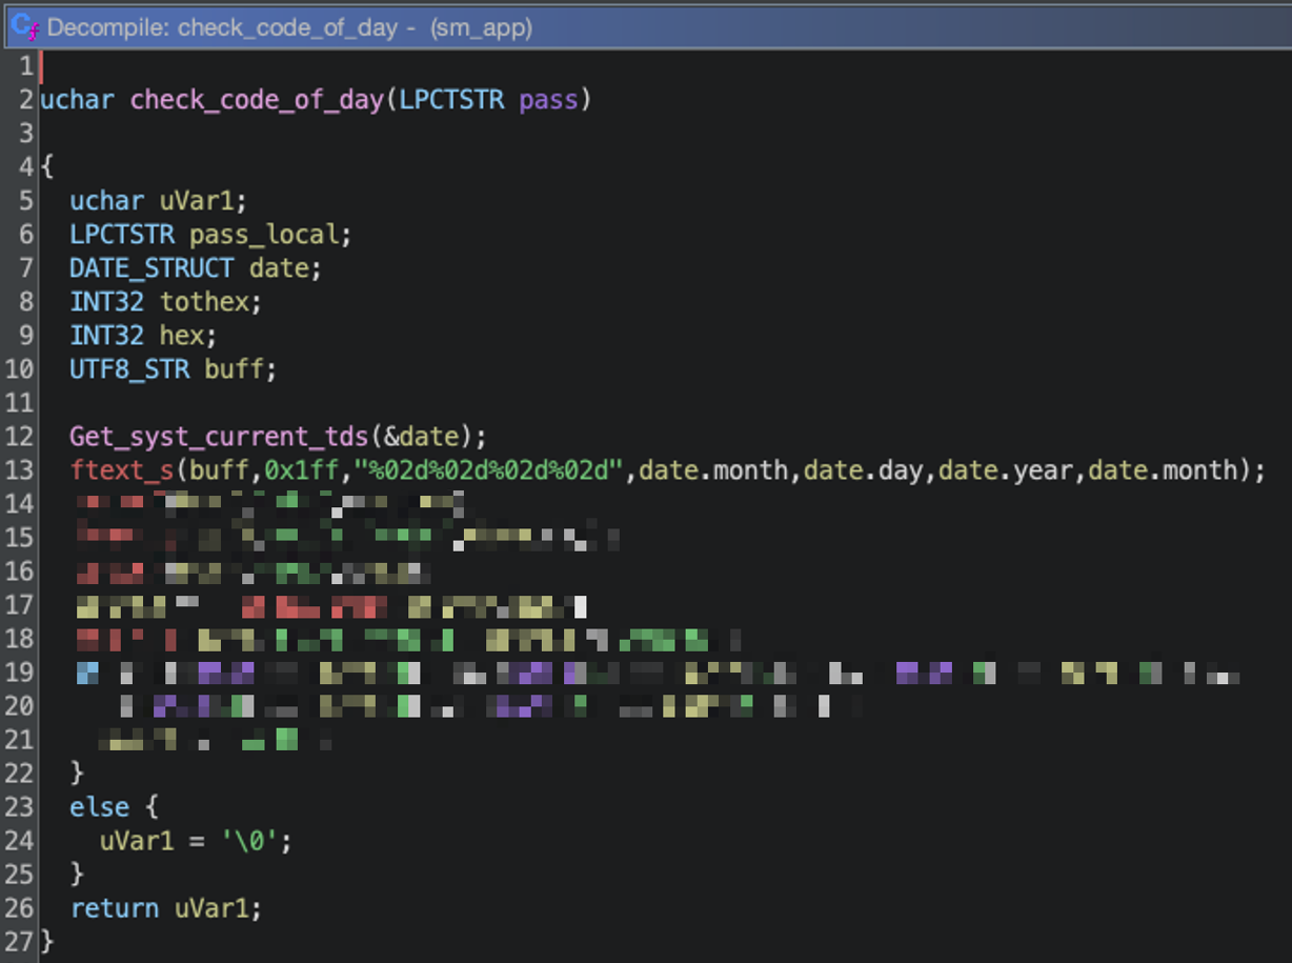
Just to add: hard coded in terms of the mathematical formula for the password was hard coded "code-of-the-day", in the article I linked (system serial + current day => same algorithm => master password, and serial number was easy to get).
The issue is that the older models it was a firmware patch, so had to be done manually for each one, and flashing the firmware lost all profiles/settings, so recalibrate etc., all of it, not being able to use any of the fridges anymore.
Still unsure why other guards weren't put in place so they can't connect to the internet etc. if known.
I got a chance to read the full article. These 'white hat' hackers are extremely thorough at indentifying all of the vulnerabilities in a system. It's a pity this only happens after they are deployed at scale in a live environment.
The whole point of the expensive controllers was to connect to the Internet for monitoring. IMO it was a security failure, not a design oversight.
The loss of stored food was expensive, but the unavailability of those fridges until they are upgraded may be even more costly.


